

The cart is empty
Hosting blog
-
MyDreams VPS Hosting

- Hosting blog

13
Sep
Sep
How to Write SEO Content with AI According to Google E-E-A-T
Artificial intelligence can now create articles, product descriptions, tutorials, and expert content within minutes. However, if you want AI-generated content to be useful, trustworthy, and suitable for SEO, it is not enough to simply ask ChatGPT or another AI tool to “write an SEO article.” Modern SEO is increasingly focused on content quality, usefulness, expertise, and trust.…
31
Aug
Aug
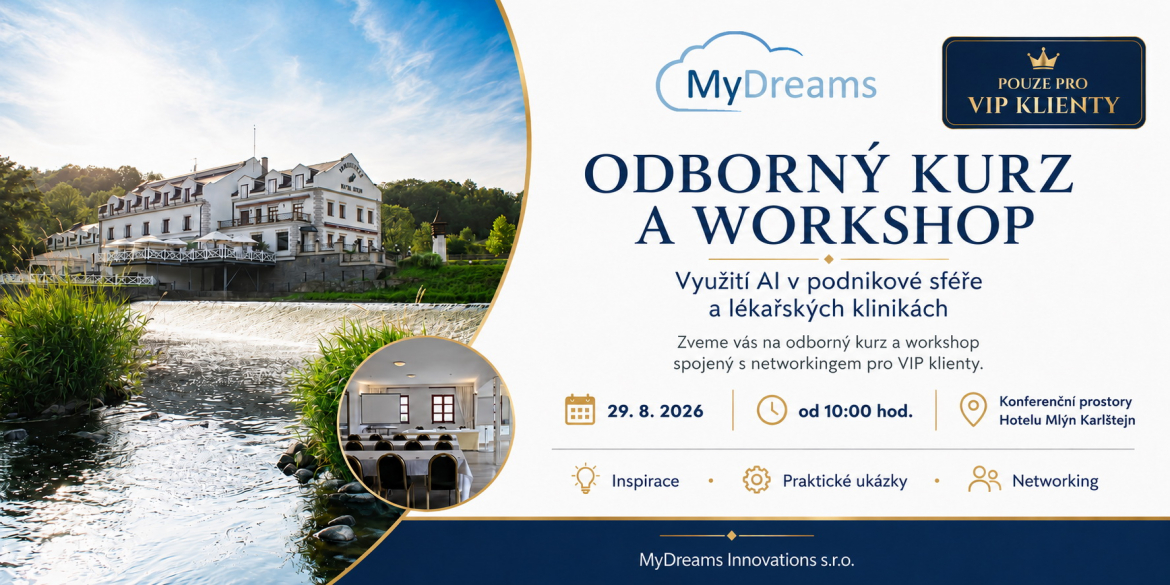
We hosted a Exclusive AI Seminar and VIP Client Meeting
On August 29, 2026, MyDreams Innovations s.r.o. organized a professional seminar followed by an afternoon networking meeting for its key VIP clients. The event took place from 10:00 AM in the conference facilities of Hotel Karlštejn. The main topic of the professional session focused on the current possibilities of using artificial intelligence in the business environment. The…
20
Jul
Jul
Critical wp2shell Vulnerability in WordPress: Update Your Website Immediately
WordPress has released an emergency security update that fixes a critical vulnerability chain known as wp2shell. The security issue allows a remote attacker to compromise certain Wordpress installations without knowing a password, without having a user account, and even without any vulnerable plugin or theme being installed. The issue primarily affects websites running WordPress versions 6.9.0 through…
14
Jul
Jul
Critical Vulnerability in Helix Ultimate 2.2.6 and Older Versions: Malicious JavaScript Can Take Over Joomla Administration
A serious security vulnerability has been discovered in the popular Helix Ultimate framework for Joomla. The flaw allows an unauthenticated attacker to write data into menu item parameters and inject malicious JavaScript into a website. The vulnerability affects Helix Ultimate 2.2.6 and all older versions. The security fix was released in version 2.2.7. However, we recommend always…
09
Jul
Jul
Critical vulnerability CVE-2026-54807 threatens WordPress e-commerce sites using WooCommerce
A critical security vulnerability identified as CVE-2026-54807 has been discovered in the Registration Form for WooCommerce plugin. The vulnerability may allow an unauthenticated attacker to obtain administrator privileges and subsequently take control of the entire Wordpress website. The vulnerability received a CVSS score of 9.8 out of 10, placing it in the highest category of critical security…